csplit -z -f msg /var/spool/mail/root ‘/^From /’ ‘{*}’
less $(ls msg* | tail -n 1)
tac /var/spool/mail/root | awk ‘/^From /{exit} {print}’ | tac
Linux Tutorial and something else…..
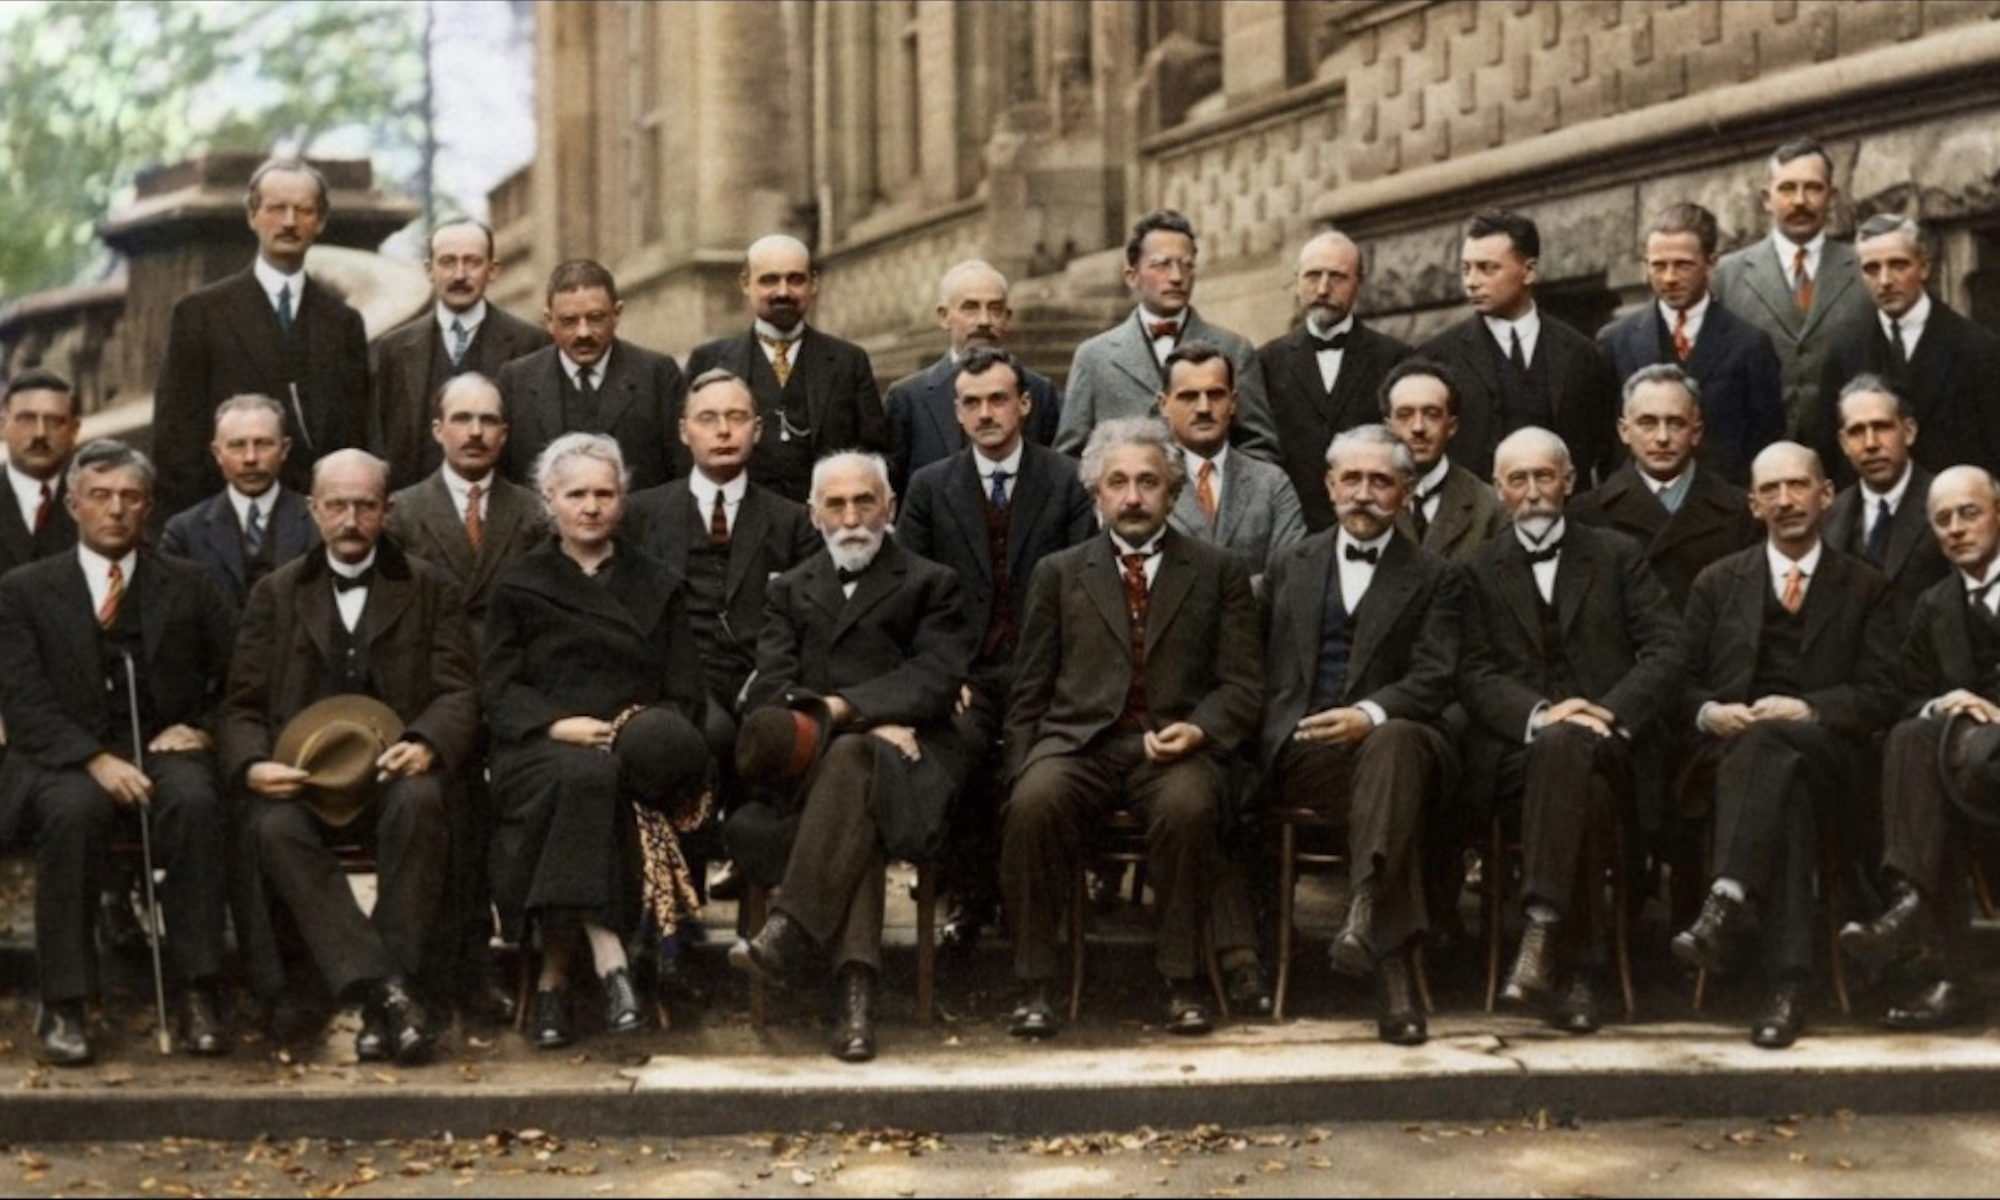
I don't know what's the matter with people: they don't learn by understanding, they learn by some other way — by rote or something. Their knowledge is so fragile! (Feynman). Auguste Piccard, Émile Henriot, Paul Ehrenfest, Édouard Herzen, Théophile de Donder, Erwin Schrödinger, Jules-Émile Verschaffelt, Wolfgang Pauli, Werner Heisenberg, Ralph Fowler, Léon Brillouin. Peter Debye, Martin Knudsen, William Lawrence Bragg, Hendrik Anthony Kramers, Paul Dirac, Arthur Compton, Louis de Broglie, Max Born, Niels Bohr. Irving Langmuir, Max Planck, Marie Curie, Hendrik Lorentz, Albert Einstein, Paul Langevin, Charles-Eugène Guye, Charles Thomson Rees Wilson, Owen Willans Richardson.
csplit -z -f msg /var/spool/mail/root ‘/^From /’ ‘{*}’
less $(ls msg* | tail -n 1)
tac /var/spool/mail/root | awk ‘/^From /{exit} {print}’ | tac
Position file in nexcloud data folder : /var/www/nextcloud/data/NOMEUTENTE/files/
sudo chown -R www-data:www-data /var/www/nextcloud/data/NOMEUTENTE/files/cartella/file.zip
from the root of the web site of nexcloud
sudo -u www-data php occ files:scan –path=”NOMEUTENTE/files/cartella”
Basically, the /etc/shadow file stores secure user account information. All fields are separated by a colon (:) symbol. It contains one entry per line for each user listed in /etc/passwd file. Generally, shadow file entry looks as follows (click to enlarge image):

/etc/shadow file format (click to enlarge)
As with the /etc/passwd, each field in the shadow file is also separated with “:” colon characters as follows:
Find all file with permission to run if belong to wheel or sudo group. Bit suid active
find / -perm /u+s 2>/dev/null
The denied access is not visualized with 2>/del/null
Command to show who has access to a file or folder : lsof <file/folder name>
Is possible to use the command fuser <file name>
sudo visudo manage the user permission
id user for check the groups
ulimit -a check the limit and set it for single user
to set the limit in global level user : /etc/security/limits.conf
journalctl -eu docker