fail2ban-client set postfix unbanip 32.227.233.171
how to show jail list :
fail2ban-client status
List of banned or recidive ip
iptables -L -n

Linux Tutorial and something else…..
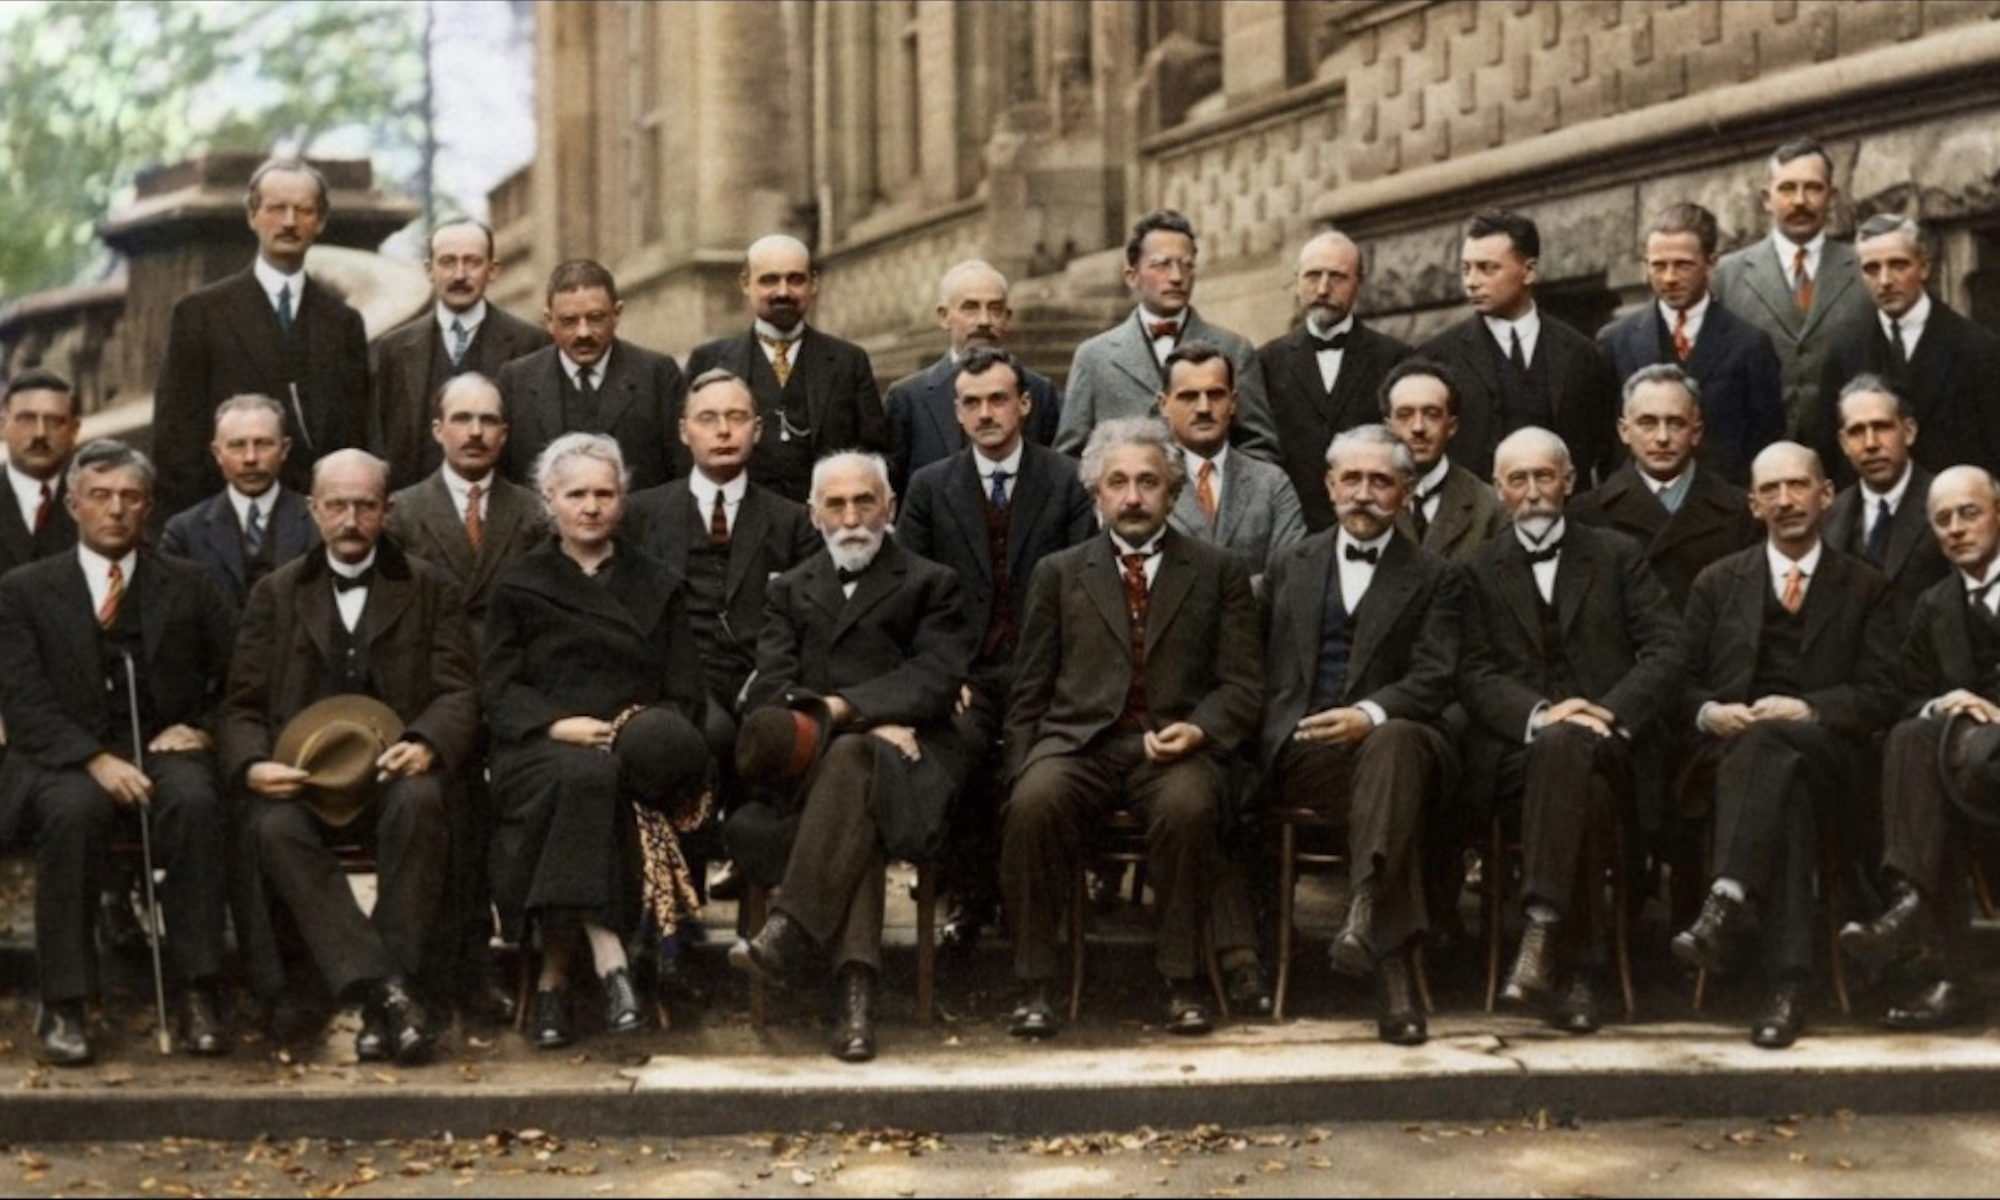
I don't know what's the matter with people: they don't learn by understanding, they learn by some other way — by rote or something. Their knowledge is so fragile! (Feynman). Auguste Piccard, Émile Henriot, Paul Ehrenfest, Édouard Herzen, Théophile de Donder, Erwin Schrödinger, Jules-Émile Verschaffelt, Wolfgang Pauli, Werner Heisenberg, Ralph Fowler, Léon Brillouin. Peter Debye, Martin Knudsen, William Lawrence Bragg, Hendrik Anthony Kramers, Paul Dirac, Arthur Compton, Louis de Broglie, Max Born, Niels Bohr. Irving Langmuir, Max Planck, Marie Curie, Hendrik Lorentz, Albert Einstein, Paul Langevin, Charles-Eugène Guye, Charles Thomson Rees Wilson, Owen Willans Richardson.
fail2ban-client set postfix unbanip 32.227.233.171
how to show jail list :
fail2ban-client status
List of banned or recidive ip
iptables -L -n
Hi,
from logwatch I saw this error :
ERROR Failed to execute ban jail ‘ssh-iptables’ action ‘iptables’ info ‘CallingMap({‘ipjailmatches’: <function <lambda> at 0x7f8e24d2b578>, ‘matches’: u’Jan 28 00:15:51 saic sshd[30705]: pam_unix(sshd:auth): authentication failure; logname= uid=0 euid=0 tty=ssh ruser= rhost=ti0100a400-1587.bb.online.no user=root\n
Failed password for root from 85.165.177.58 port 45430 ssh2\n
Failed password for root from 85.165.177.58 port 45430 ssh2′, ‘ip’: ‘85.165.177.58’, ‘ipmatches’: <function <lambda> at 0x7f8e24d2b488>, ‘ipfailures’: <function <lambda> at 0x7f8e24d2bb90>, ‘time’: 1485558957.444361, ‘failures’: 3, ‘ipjailfailures’: <function <lambda> at 0x7f8e24d2b5f0>})’: Error starting action
To solve I follow this : https://github.com/fail2ban/fail2ban/issues/973
and than this : https://github.com/fail2ban/fail2ban/issues/878#issuecomment-65732113
Not necessarily… But if you will really stand-alone fail2ban, so download direct from github or checkout via git (from github). – master – https://github.com/fail2ban/fail2ban/archive/master.zip – debian – https://github.com/fail2ban/fail2ban/archive/debian.zip – repo – git://github.com/fail2ban/fail2ban.git
Hereafter unzip it and run install:
cd /tmp/f2b
?sudo? python setup.py install
So I reinstalled fail2ban, previous backup fine (/etc/fail2ban).
After installation I overwrote /etc/fail2ban with my previous file.
a) Create configuration file
vim /etc/fail2ban/filter.d/wordpress.conf
# Fail2Ban filter for WordPress hard failures
#
[INCLUDES]
before = common.conf
[Definition]
_daemon = (?:wordpress|wp)
failregex = .*<HOST> – – .* “POST \/wp-login\.php HTTP\/1\.1” 200 (5127|5128|5129|5130) .*
.*<HOST> – – .* “POST \/xmlrpc\.php HTTP\/1\.1” 200 (5127|5128|5129|5130) .*
.*<HOST> – – .* “POST \/blog\/wp-login\.php HTTP\/1\.1” 200 (5127|5128|5129|5130) .*
.*<HOST> – – .* “POST \/web\/wp-login\.php HTTP\/1\.1” 200 (5127|5128|5129|5130) .*
ignoreregex =
b) set jail.conf
[wordpress]
enabled = true
filter = wordpress
action = iptables-multiport[name=wordpress, port=”http,https”, dest=postmaster@saic.it, sender=postmaster@saic.it]
logpath = /var/log/httpd/access_log
maxretry = 5
port = http,https
findtime = 300
bantime = 10800
restart failban
vi /etc/fail2ban/filter.d/ispconfig.conf
The first thing we need to do is create a filter for ISPconfig in the /etc/fail2ban/filter.d/ directory.
vi /etc/fail2ban/filter.d/ispconfig.conf
Add the following definition so the filter knows what to look for in the /var/log/ispconfig/auth.log for ISPConfig 3.
# Fail2Ban filter for ISPConfig hard failures
#
[INCLUDES]
before = common.conf
[Definition]
_daemon = (?:ispconfig)
failregex = Failed login for user .* from <HOST>
ignoreregex =
vim /etc/fail2ban/jail.conf
add this line
[ispconfig]
enabled = true
port = 8080
filter = ispconfig
action = iptables-multiport[name=wordpress, port=”http,https”, dest=postmaster@saic.it, sender=postmaster@saic.it]
logpath = /var/log/ispconfig/auth.log
maxretry = 3
findtime = 300
bantime = 10800
You can/should test the new configuration by running the following command.
fail2ban-regex /var/log/ispconfig/auth.log /etc/fail2ban/filter.d/ispconfig.conf
THEN Restart fail2ban to load your new jail for ISPConfig 3 failed login attempts.
service fail2ban restart
usefull
Today I found an error in the regular expression of failban filter :
/etc/fail2ban/filter.d/postfix-sasl.conf
with this useful site https://regex101.com/ gave me an error so I changed the expression from
failregex = ^%(__prefix_line)swarning: [-._\w]+\[<HOST>\]: SASL ((?i)LOGIN|PLAIN|(?:CRAM|DIGEST)-MD5) authentication failed(: [ A-Za-z0-9+/:]*={0,2})?\s*
failregex = ^%(__prefix_line)swarning: [-._\w]+\[<HOST>\]: SASL ((?i)LOGIN|PLAIN|(?:CRAM|DIGEST)-MD5) authentication failed(: [ A-Za-z0-9+\/:]*={0,2})?\s*
failban conf file : jail.conf
[postfix-sasl]
enabled = true
filter = postfix-sasl
action = iptables[name=postfix-sasl, port=”smtp,465,submission,imap3,imaps,pop3,pop3s”, protocol=tcp]
sendmail-whois[name=postfix-sasl, dest=postmaster@saic.it, sender=postmaster@saic.it]
#port = smtp,465,submission,imap3,imaps,pop3,pop3s
# You might consider monitoring /var/log/mail.warn instead if you are
# running postfix since it would provide the same log lines at the
# “warn” level but overall at the smaller filesize.
logpath = %(postfix_log)s
backend = %(postfix_backend)s
maxretry = 3
bantime = 10800
here /etc/fail2ban/paths-fedora.conf the configuration of the variable postfix_log and postfix_backend
http://www.fail2ban.org/wiki/index.php/Fail2ban:Community_Portal